GitHub Code scanning AI Scan for PRs is generally available, covering languages CodeQL does not
On October 15, 2026 GitHub made Code scanning AI Scan for pull requests generally available. It finds vulnerabilities in PR changes for languages and frameworks CodeQL does not yet cover; findings are advisory and do not block merges.
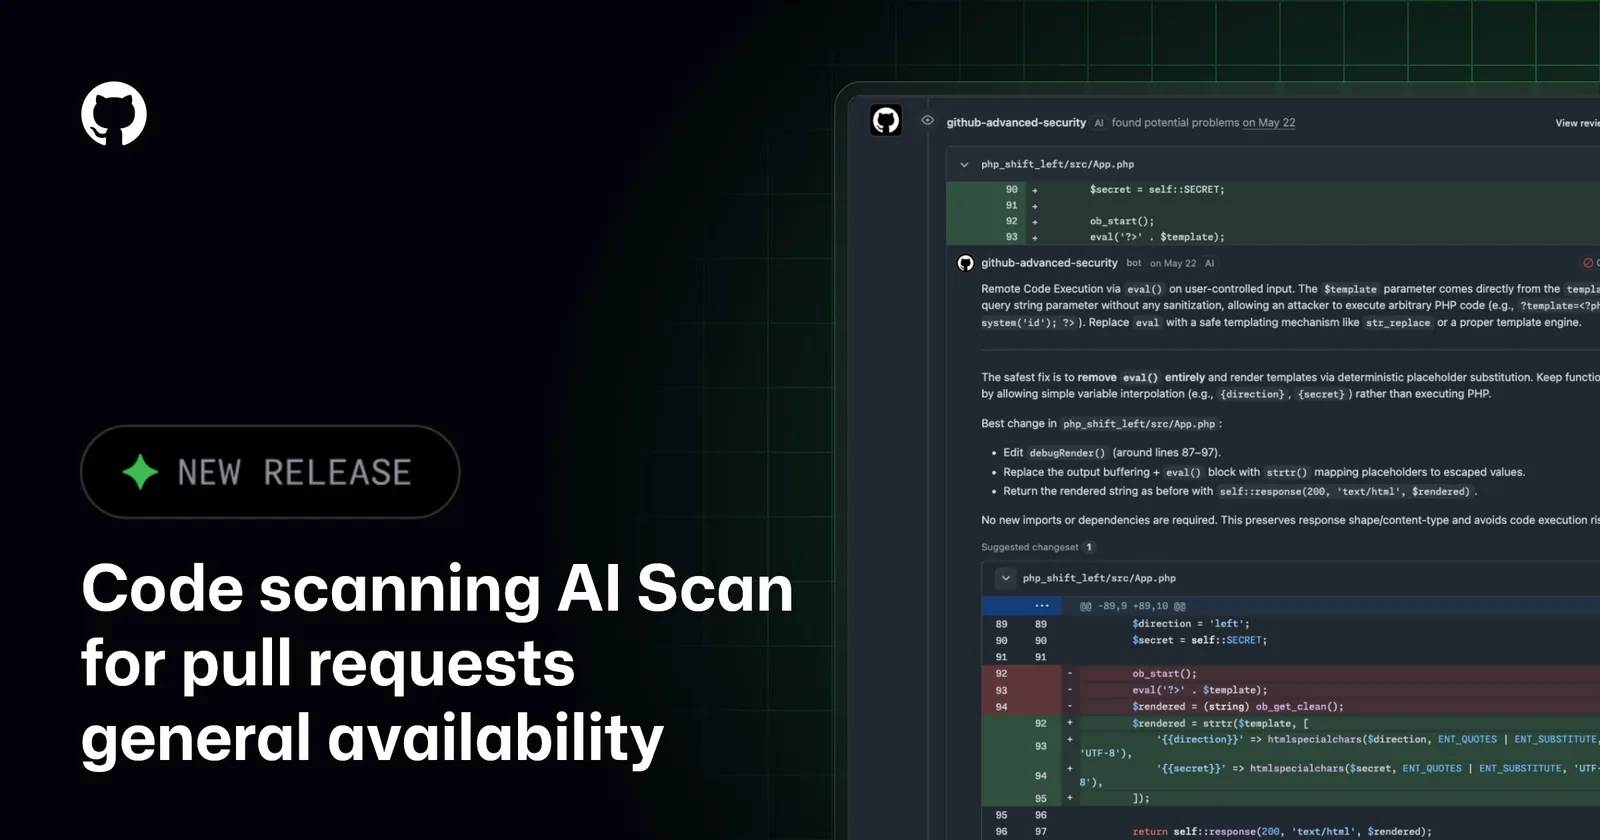
GitHub announced on October 15, 2026 that Code scanning AI Scan for pull requests is generally available. It complements CodeQL by finding vulnerabilities in pull request changes for languages and frameworks CodeQL does not currently cover, including PHP, Shell/Bash, Terraform configuration (HCL), Dockerfiles, JSP for Java, Blazor for C#, and more.
AI Scan runs automatically on pull requests when code scanning and the repository’s effective AI Scan setting are enabled. Findings appear on the Conversation and Files changed tabs with an “AI” indicator, and can include a risk explanation and a suggested autofix. GitHub says findings are advisory: they do not fail the code scanning check and cannot block merges via ruleset requirements. AI Scan does not run on pull requests from forks or Dependabot-created pull requests.
Availability: public repositories owned by organizations or personal accounts. Private and internal organization-owned repositories require GitHub Code Security or GitHub Advanced Security. A Copilot license is not required. Billing: AI Scan for pull requests consumes Code Security AI Credits, shown under Advanced Security in enterprise AI usage, with optional SKU-level budgets.
Sources
- AI Scan for pull requests generally available — GitHub Changelog